NetSuite SuiteCloud Development Framework Release Controls
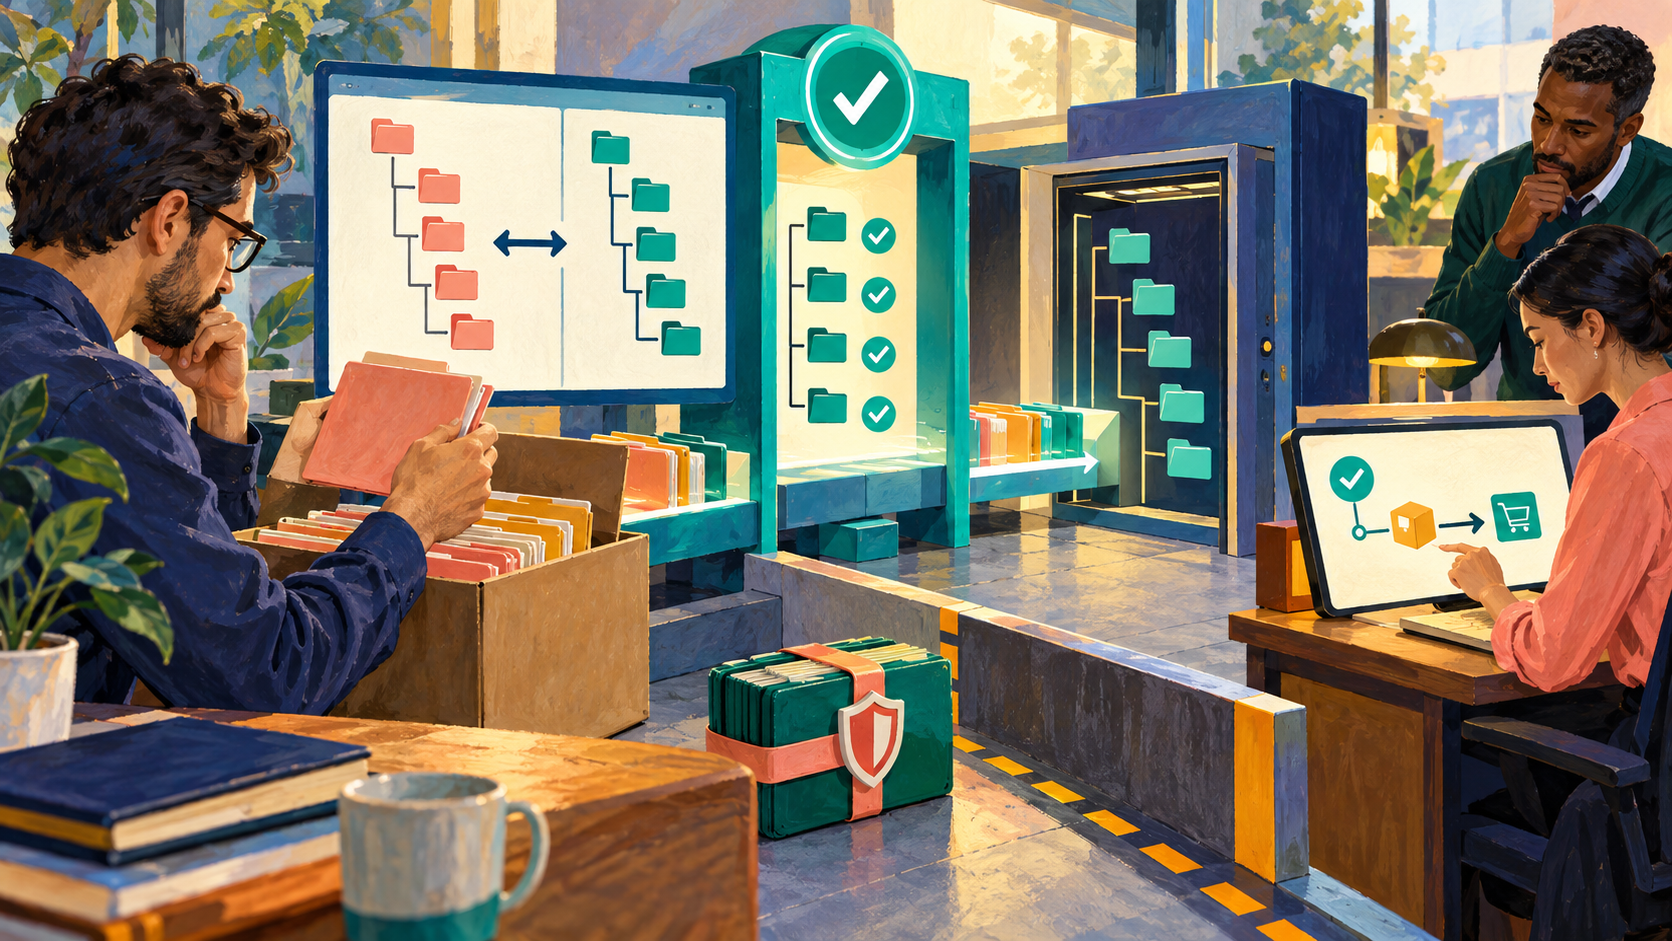
Control an SDF release by promoting an identified set of reviewed files and object definitions, validating against the intended NetSuite account and checking the business result after deployment. Keep the target account, dependencies and recovery boundary explicit. A passing validation log establishes useful technical checks, but it does not prove that the change implements the right business rule.
SuiteCloud Development Framework represents supported account customizations as file-based projects. That makes versioned review possible, but it also makes accidental overwrites possible when local definitions do not reflect current production state. The release process must connect repository evidence to what actually exists in the account.
Establish the source of truth before packaging
Identify the approved repository commit or release artifact. Record who reviewed it and which request it implements. Avoid promoting whatever happens to be on a developer's workstation after a successful demonstration.
Compare the current target state with the baseline assumed by the change. Another administrator may have adjusted a form, workflow or field directly in the account since the branch was created. Resolve that drift before deployment rather than allowing the older local definition to erase it.
SDF objects overwrite target objects with matching script IDs, while matching files and scripts can replace earlier File Cabinet versions. Stable identifiers therefore need ownership. A renamed label does not necessarily create a new object, and a new file name does not automatically redirect existing deployment references.
Record components managed by another provider. Locked objects and installed-application boundaries can constrain what an account-customization project may change. Escalate those dependencies through the supported owner instead of trying to work around protection.
Limit the release to a coherent change
Define the release unit in terms of behavior. A new workflow may require a custom field and a saved search to move together, while an unrelated form cleanup can wait. Bundling unrelated changes increases the number of explanations needed if the result fails.
Review the deployment manifest and included files. For each object, identify whether it is new, modified or an existing dependency. A dependency that is already correct in production should not be treated casually as an opportunity to overwrite it from an older sandbox.
List manual or unsupported steps separately. SDF support is not a claim that every account setting, transaction or external-system configuration belongs in the project. The runbook should show the complete release sequence, including work outside the deployable package.
Assign an owner to each step and define the verification needed before moving on. A mixed release can fail even when the SDF portion succeeds if a required mapping or permission change is omitted.
Validate against the correct account
Check the authentication profile and account identifier immediately before validation and deployment. Similar sandbox and production names are a practical risk. Keep the target evidence in the release record without exposing credentials.
Server-side validation examines feature and file dependencies, object definitions, required values and other supported constraints. Review warnings as well as errors. Explain any accepted warning rather than treating a successful process exit as blanket approval.
For the Node.js CLI, the account-specific-values validation option can classify those values as warnings or errors. Default behavior does not automatically enforce the stricter policy a team may expect. Set and document the intended policy, using the version of the tooling actually deployed.
Validate close to the release. An earlier sandbox pass cannot prove that production has the same enabled features, values or dependencies. Equally, a current validation does not run the organization's entire approval, billing or reporting process.
Keep functional acceptance separate
Tie tests to the changed behavior and its important consumers. If a field becomes mandatory, check user entry, CSV import and relevant integrations. If a workflow condition changes, test eligible and ineligible records and the intended business role.
Use expected outcomes that another reviewer can inspect. Examples include a correctly assigned approver, unchanged financial totals, a denied unauthorized action or a single downstream record for one event. “Deployment completed” is not a functional result.
Preserve the version of the test data and account configuration. A passing case with a different feature set or role may be useful background but insufficient acceptance evidence for the production change.
Avoid interpreting validation as a guarantee that no deployment-time error can occur. Some checks and account interactions arise at deployment or runtime. The runbook needs a response to partial or unexpected outcomes, not merely a path for the ideal case.
Hypothetical example of a hidden overwrite
A fictional team plans to deploy eight changed objects: one workflow, two fields, three forms and two saved searches. The package includes those eight plus four dependencies, producing 12 objects for review.
During the target comparison, the reviewer discovers that one of the four dependencies contains a production-only correction. Deploying the stale dependency would undo an approved change even though the new workflow itself passed testing. The team reconciles the definition and repeats the affected tests before release.
The deployment log then identifies 12 installed objects with no unexpected additions. Functional checks cover five critical business scenarios, of which four pass and one fails because a downstream report uses an old field meaning. The release remains under incident handling despite its technically successful deployment.
The response is to stop the affected process, assess records already created and choose an approved correction. A count of 12 installed objects proves neither that five scenarios passed nor that earlier business effects can be erased safely.
Define recovery before the deploy command
Preserve the previous approved definitions and explain how they would be redeployed where supported. Verify that the recovery artifact is available to the person responsible for using it. A repository link is insufficient if nobody knows which version represents the prior working state.
Separate configuration recovery from data correction. Restoring a workflow definition does not automatically reverse records, notifications or external requests that the new version already produced. Identify the first consequential action after which recovery requires business reconciliation.
For a newly introduced field or custom record, retaining it temporarily may be safer than immediate deletion. Decide historical-data and dependency treatment with the business owner. Do not describe removing a file from a project as a universal instruction to remove its account object.
Define stop criteria and authority. A failed critical permission test or unexplained transaction result should trigger the agreed response even if most checks are green. The person deploying should not need to invent a risk-acceptance policy during the window.
Read deployment evidence and verify the running state
The Deployment Audit Trail provides installation logs containing installed objects and files, timestamps, warnings and errors. Retain that evidence alongside the approved artifact and target account. Inspect what was installed rather than recording only that a command ran.
Confirm that relevant deployments point to the intended files and that enabled state, parameters and roles match the release plan. A new source file can exist in the File Cabinet while an active deployment still references an earlier file.
Run the agreed safe production checks and observe the first relevant business cycle. For a scheduled process, the release is not fully accepted until its required execution and output have been examined or an explicitly approved alternative test has established the result.
Document any difference between the planned and actual release. Bring approved emergency changes back into the maintained source so the next promotion does not undo them.
Leave a release record someone else can use
Retain the request, artifact version, component list, target comparison, validation results, approvals, deployment log, functional evidence and recovery decision. Keep secret material in its designated secure system and reference it only by approved identifiers.
Where SDF deployment has become difficult to explain, CuriousRubik's NetSuite support services can help review the release boundaries and account dependencies. The aim is a repeatable link from approved change to deployed behavior, with honest limits on what technical validation establishes.
Frequently asked questions
Does successful SDF validation prove the release is safe?
It confirms supported technical checks against the selected target. Business rules, permissions, external effects and end-to-end outcomes still require appropriate testing and approval.
Can an SDF deployment overwrite an existing customization?
Yes. Matching script IDs and file names can replace earlier target definitions or files. Compare the target with the assumed baseline and resolve production drift before promotion.
Should account-specific values always be ignored?
No. Set an explicit validation policy appropriate to the project and target. Review the available tooling options and explain accepted warnings rather than relying on defaults.
Is rollback the same as reversing transactions?
No. Restoring configuration does not undo consequential records or external messages already produced. Define a separate reconciliation and approved correction plan for those effects.
What should be retained after deployment?
Keep the approved artifact version, target account, validation and installation logs, component inventory, business-test evidence and any recovery or exception decisions. Together they explain what actually changed.
Related reading