NetSuite SuiteApp Due Diligence Before Installation
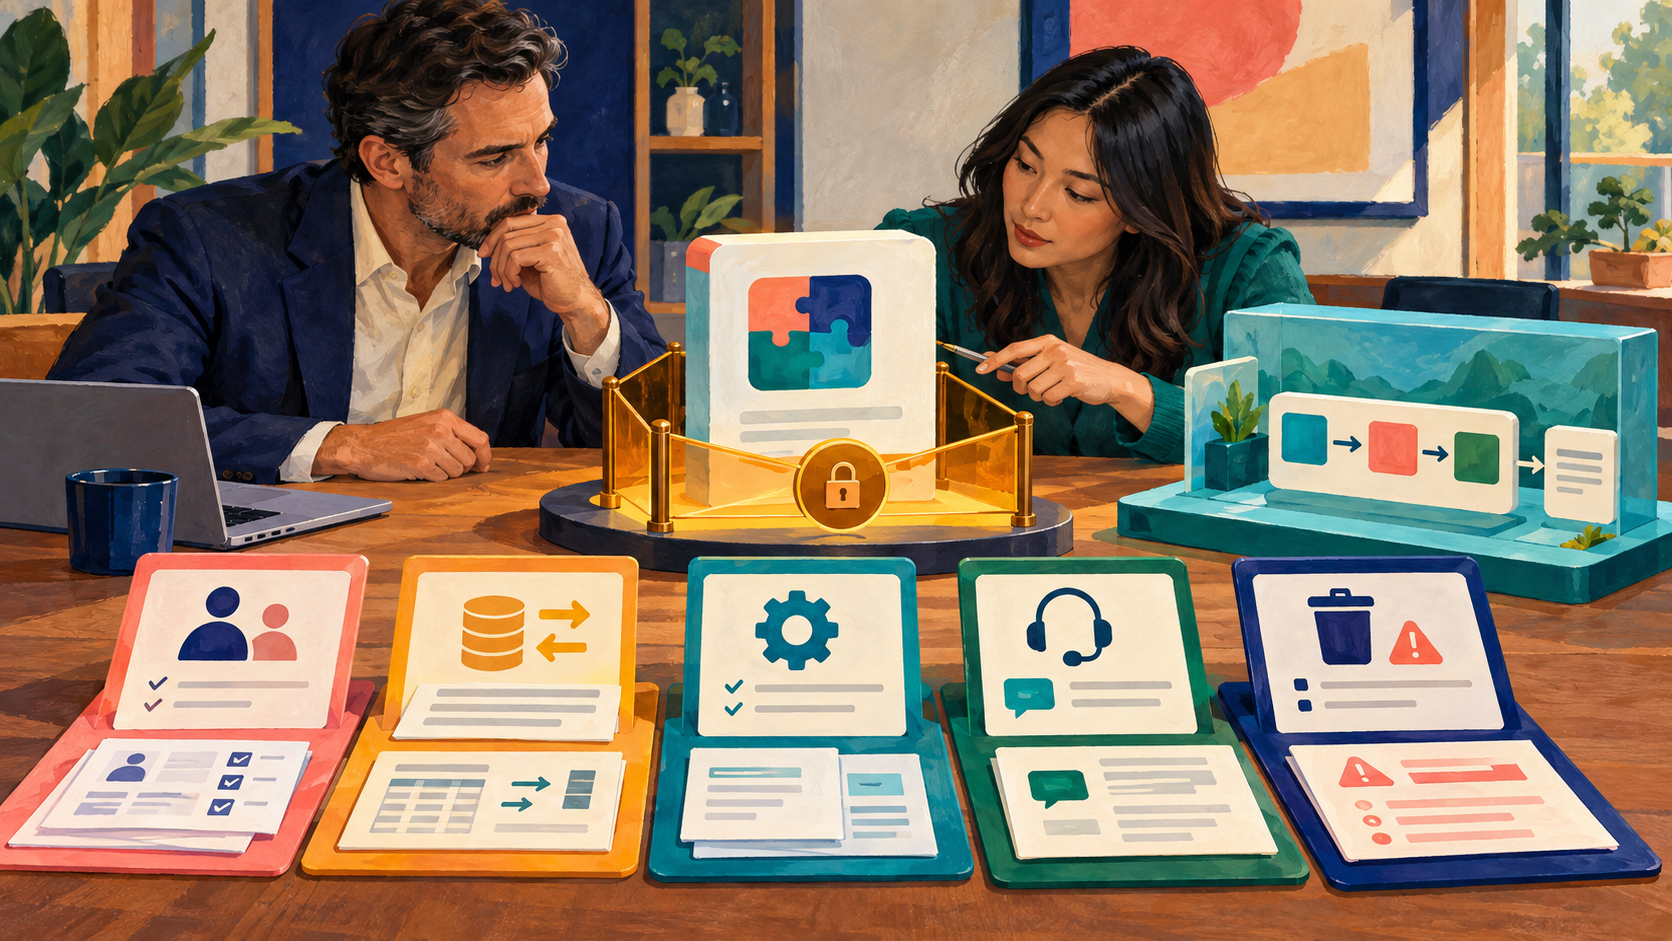
Evaluate a NetSuite SuiteApp by proving its fit for a specific business process and understanding the access, data movement, account changes and ongoing obligations that installation introduces. A successful demonstration is useful, but approval should depend on the proposed operating model, exception handling and exit plan as well as the visible features.
Begin before the installation request reaches an administrator. Some packages alter existing configuration, some receive provider-managed updates and some retain important data in custom objects. Treat the application as a maintained dependency with a business owner, rather than as a reversible experiment just because an Install button is available.
Describe the job the application must do
Write the current problem as a measurable process gap without inventing a promised improvement. Specify the trigger, records, users, desired outcome and known exceptions. “Automate purchasing” is too broad to test; “route approved requests into purchase orders while retaining authorized supplier and cost-center choices” is concrete.
Separate essential requirements from preferences. Identify which cases must work on day one and which can use a controlled workaround. Ask the provider to demonstrate those cases with a realistic test configuration, including an error or rejected transaction.
Consider whether existing NetSuite configuration already supports the need. A standard feature, a small supported customization or a process change may have a different maintenance burden. Compare options against the same outcomes rather than comparing a polished demonstration with an undocumented description of the alternative.
Name the process owner who will accept the result. Technical installation success is not the same as business acceptance, particularly when the application affects posting, approvals or customer communications.
Identify the actual package and installation route
Record the provider, application identifier, version, distribution route and target account. A marketplace name can refer to several versions or related bundles. Confirm which components will be installed and which prerequisites must already exist.
SuiteBundler customization bundles create account objects. Configuration bundles copy settings and can overwrite existing configuration. Managed bundles introduce provider-driven updates, and configuration bundles cannot simply be uninstalled. These distinctions belong in the approval record before installation.
SDF-distributed SuiteApps have their own installation status and deployment evidence. Do not assume that every application uses the same lifecycle controls because all are described commercially as SuiteApps. Ask the provider to identify the supported installation, upgrade and recovery procedures for the exact product.
Review conflicts with existing object names or script identifiers. Resolve ownership before choosing any replacement behavior. An application should not quietly take control of an existing field or workflow whose meaning another team depends on.
Trace the data from entry to storage
Ask where each important record is stored and processed. The answer may include NetSuite custom records, an external service, an integration platform and a provider's support systems. Record the purpose and minimum data required at every boundary.
Inspect outbound data categories, attachment handling, logging and support access. A statement that an application is “native” does not by itself answer whether it sends telemetry, documents or diagnostic payloads elsewhere. Request a concrete data-flow explanation and the relevant contractual information for the organization's reviewers.
Separate ordinary configuration values from credentials. Confirm who provisions and rotates any application authorization, who can use it and how it is revoked. Do not put secret values in the evaluation spreadsheet or ask the provider to email them to the project team.
Define retention and export needs before loading meaningful data. If the application owns a calculation history or approval trail, the organization should know how it can retain and interpret that evidence after the subscription ends.
Challenge the permission request
Request a permission list tied to operations. The provider should explain why a role needs to view, create, edit or delete each important record type, and which subsidiary or departmental restrictions are supported.
Test with the intended business roles and integration identity. An administrator-led demonstration can conceal permission gaps. Include a denied case: an unauthorized person or excluded subsidiary should remain outside the application workflow unless the business explicitly approved an exception.
Review administrative setup permissions separately from ongoing runtime permissions. A privilege needed during installation may not be necessary for daily operation. Establish the supported way to remove temporary setup access without breaking maintenance or upgrades.
Check the application's own custom-record access and external interfaces. Native role restrictions may require explicit configuration for custom objects. A familiar NetSuite form does not prove that every supporting endpoint enforces the same boundary.
Test the failure and upgrade paths
Ask what happens when a record is rejected, an external service is unavailable or a process is interrupted halfway through. Identify how support determines which work completed and what can safely be retried. For financial or fulfillment activity, reconcile the business result rather than relying on a green application status.
Clarify release responsibility. Who tests new NetSuite releases, who validates provider updates and how are customers notified of material changes? For managed updates, understand the actual controls available to your account instead of assuming every update can be delayed indefinitely.
Review support ownership across the provider, implementation partner, internal administrator and Oracle. Define the evidence each party needs and which party coordinates a cross-system incident. A contract promising a response is different from a promise that the underlying business process will be restored by that time.
Confirm how configuration changes are documented. If the provider's support team adjusts a mapping during diagnosis, the business still needs a record of what changed and how the intended result was checked.
Hypothetical example of a purchasing application review
A fictional company tests a SuiteApp against 18 requirements: ten essential, five important and three optional. The demonstration meets nine essential requirements, all five important requirements and all three optional requirements. That is 17 of 18 overall, or about 94.4%.
The missing essential requirement is rejection of a request for an unauthorized subsidiary. The high overall score does not justify installation into production because the failed case affects the approved access boundary. The team holds the decision until the provider demonstrates an acceptable supported design.
A second review identifies 12 installed custom objects, including two custom-record types that store approval evidence. The exit plan therefore needs more than uninstall instructions. It must define an approved export, relationships needed to interpret the records and verification that the retained evidence is readable.
The example is hypothetical. Its point is to keep critical gates separate from aggregate scoring and to consider data ownership before the application becomes embedded in daily work.
Treat removal as a separate project
Uninstalling a customization bundle can delete bundled objects and their data, including custom-record instances. Some replaced or shared objects can remain. Related workflows may also be changed by removal. Consequently, uninstall is not a universal rollback to the account's earlier state.
Ask the provider to explain what remains, what disappears and what must be preserved first. Rehearse the approved exit procedure in a suitable non-production environment. Include the consumers of the application's data, not only the application screen.
Retain evidence of the accepted version, permissions, configuration, tests, owners and exit requirements. Keep unresolved questions visible with a decision owner. A vendor answer that is still pending should not become an assumed capability in the sign-off.
A focused assessment with CuriousRubik's NetSuite support services can turn the evaluation into a practical acceptance pack. Procurement, security, finance and process owners should approve the obligations and risks relevant to their responsibilities.
Frequently asked questions
Is a marketplace listing enough to approve a SuiteApp?
No. Evaluate the exact application's process fit, permissions, data flows, support responsibilities, updates and exit behavior. A listing does not establish suitability for your account's controls.
Are all SuiteApps uninstalled in the same way?
No. Identify the distribution and package type. Configuration bundles cannot simply be uninstalled, and removal of customization bundles can delete objects and stored data.
Should the provider receive Administrator access for everyday use?
Require an explanation of the minimum supported permissions. Separate temporary setup needs from runtime access and test the intended restricted roles rather than accepting broad access by default.
What should an upgrade test include?
Run essential business cases, meaningful failures, role boundaries and reconciliation of consequential outputs. Verify the provider's supported update controls and document who accepts the result.
What is the most important exit question?
Determine how the organization will retain and interpret its required data and evidence after the application is removed or the contract ends. Verify that plan before important records accumulate.
Related reading