NetSuite Healthcare Back-Office Data Boundaries
A healthcare back-office implementation should send NetSuite only the information needed for approved financial and operational purposes. Keep clinical detail in the appropriate clinical systems unless a specific, reviewed design authorizes it elsewhere. Define the data boundary field by field, including attachments, free-text descriptions, error logs and exports.
That boundary is a practical implementation decision as well as a privacy concern. Finance may need an entity, service category, period and amount without needing the patient's diagnosis or treatment notes. Begin by proving the minimum information required to complete the financial task.
Separate the back-office use cases
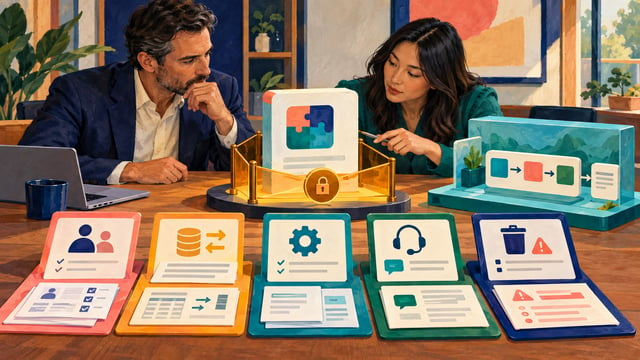
List the processes in scope: procurement, supplier invoices, payroll summaries, fixed assets, inventory, management reporting or summarized revenue. Identify the business owner and source system for each. Do not treat an interface to a clinical platform as permission to copy everything it contains.
For each process, describe the decision NetSuite users must make. A purchasing approver needs evidence of the requested supplies and budget authority. A financial reviewer needs a reproducible total and appropriate supporting references. Neither task automatically requires a patient-level clinical narrative.
Identify exceptions early. Patient refunds, payer disputes or detailed service billing may have additional data requirements. Route those cases for privacy, security and legal review instead of allowing a broad exception to become the default integration design.
Build a field-level transfer specification
For every proposed field, record its purpose, source, destination, sensitivity, retention and authorized audience. Mark it required, optional or excluded. Apply the same review to fields populated indirectly through descriptions or attachments.
Use an explicit allowed-field mapping. A connector that copies every new source field can expand the data boundary without review. Require approval before adding fields or changing the meaning of an existing one.
Review identifiers carefully. Replacing a patient name with an identifier does not automatically make the data anonymous or remove its sensitivity. Consider whether the identifier can be linked back to an individual and whether finance truly needs that link.
Confirm the contractual and service scope
NetSuite has specifically assessed services for HIPAA-related use, but that does not establish that every feature or connected application is appropriate for electronic protected health information. Confirm the purchased services and applicable agreements with the responsible specialists.
The current HIPAA for NetSuite service description requires an executed NetSuite business associate agreement, a HIPAA-assessed service and purchased, installed Compliance 360 before storing ePHI. It also restricts ePHI of non-US residents and leaves customer controls and compliance responsibilities with the customer.
Treat those requirements as matters to verify for the actual organization, service order and jurisdiction. A general product label or a completed security questionnaire is not a substitute for that review. This article is an implementation framework, not a legal compliance opinion.
Include the hidden paths data can take
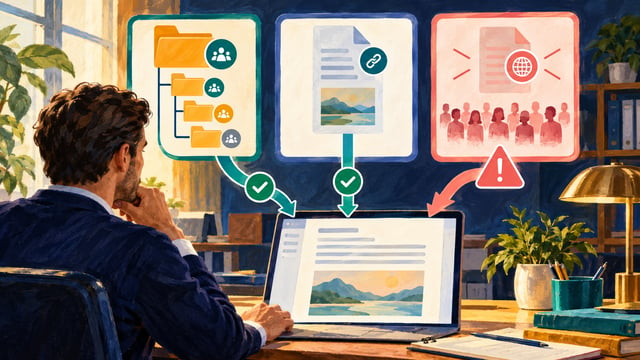
Inspect invoice attachments, file names, memo fields, support cases, email notifications and exported reports. Sensitive information can enter through these paths even when the formal integration mapping is minimal.
Check failure handling. An integration may place the entire rejected source payload in a log or support ticket. Design error records to expose the information needed for diagnosis without unnecessarily reproducing the underlying clinical data.
Review test and training environments. Production refreshes, copied spreadsheets and demonstration screenshots can move data beyond the intended audience. Use synthetic or appropriately approved test data and verify the process used to prepare it.
A hypothetical summarized revenue feed
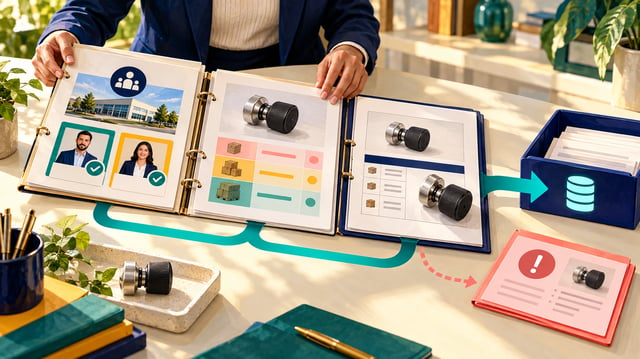
Assume a fictional healthcare group needs daily revenue totals by legal entity and service category. The source system contains 2,400 patient-level transactions. Finance approves a feed containing 24 summary lines with entity, date, category, currency and amount, plus a batch reference held in the source system.
The source control total is USD 186,000. Two invalid category mappings totaling USD 1,500 are rejected into a restricted operational queue. The accepted NetSuite batch totals USD 184,500, and accepted plus rejected activity reconciles to USD 186,000.
The rejection log records the batch and mapping problem without copying patient names or clinical descriptions. Authorized source-system staff investigate the two exceptions and provide corrected financial mappings. The example does not assume that aggregation automatically makes every data set anonymous; the privacy owner still assesses the actual fields and context.
These values are hypothetical. The control demonstrates completeness while preserving the approved data boundary, rather than using patient-level detail as a shortcut to reconciliation.
Test access at the points of use
Verify what finance, procurement, local management, administrators and integration users can see. Test searches, reports, exports and attachments in addition to transaction forms. A hidden field on one form is not sufficient evidence that the data is inaccessible elsewhere.
Confirm separation between subsidiaries or facilities where required. Check both ordinary operations and emergency support access. Record who approves expanded access, its purpose and how it is removed when the need ends.
Avoid shared user identities for convenience. Named access and appropriate role design support accountability, but controls must be validated in the configured account. Test the real user workflows rather than relying only on an administrator's view.
Design audit and retention coverage explicitly
List the activities that need evidence: record changes, access, exports, integration transfers and administrative actions. Map each requirement to a verified capability or another approved control. An audit trail for modifications does not automatically prove that every read or export is logged.
Review retention across the complete chain, including integration queues, backups, attachments and support systems. Deleting a field from an interface does not remove copies already stored elsewhere. Obtain the appropriate approval and specialist guidance for any consequential cleanup.
Establish an escalation route for unexpected sensitive data. The operator should know how to restrict further distribution, preserve appropriate evidence and contact the responsible privacy or security owner without circulating the material more widely.
Make the boundary part of change control
Require a data review when adding an integration, report, automation or AI-assisted workflow. A new destination or audience can change the risk even if the source fields remain unchanged. Keep the approved transfer specification current.
A CuriousRubik NetSuite integration review can begin with a synthetic sample and a field-level map. The useful outcome is a financial process that works with the minimum approved data and has demonstrable controls for exceptions.
Frequently asked questions
Does a healthcare organization need patient data in NetSuite?
Not for every back-office process. Start with the financial purpose and determine the minimum required fields. Detailed patient-related use cases require a separate approved design and review of services, agreements and controls.
Is replacing names with patient IDs enough?
No. Identifiers can still be linkable to individuals and remain sensitive. Have the privacy owner assess the actual data and context rather than assuming that a renamed or coded field is anonymous.
Does HIPAA-assessed mean every connected workflow is covered?
No. Verify the specific services, features, agreements and integrations. The organization's configuration and controls remain important, and additional functionality may fall outside the assessed service scope.
What should an integration error log contain?
Enough information to diagnose the approved financial interface, such as batch reference and mapping failure. Avoid copying full clinical payloads by default, and restrict access to any sensitive detail genuinely required for investigation.
How can finance reconcile a summarized feed?
Use source control totals, accepted totals, rejected totals and stable batch references. Authorized staff can investigate source detail in the appropriate system while finance verifies completeness without unnecessary clinical information.
Related reading